Bitget Raises Breach Estimate to $387.5M, Details Attack via Spoofed Transfers
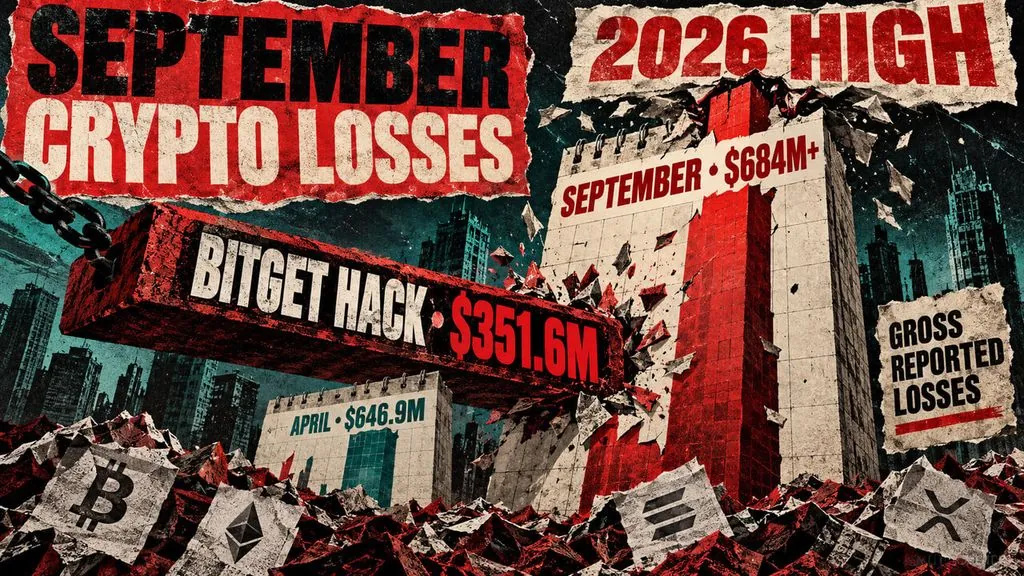
Bitget revised its security breach estimate upward to $387.5 million from an initial $351.6 million figure, according to CEO Gray Chen. The exchange said attackers exploited a wallet backend vulnerability through spoofed transaction data rather than compromised private keys, and has now fixed the flaw.
Written by CoinArticle’s AI Newsroom · from 2 cited sources. How we work
Revised Loss Figure and Attack Vector
Bitget raised its estimate of losses from the breach to $387.5 million, up from the $351.6 million figure CEO Gray Chen initially disclosed on X. Chen attributed the discrepancy to ongoing assessment of affected wallets. The attack did not involve theft of private keys but rather compromise of the exchange's wallet backend infrastructure, which allowed attackers to spoof transaction data and authorize unauthorized withdrawals.
Response and Recovery Efforts
The exchange said the underlying vulnerability has been identified and fixed. Bitget launched a recovery bounty program as part of its response, though the exchange did not disclose the bounty amount or specific terms for recovery of stolen funds. The exchange has not yet announced a timeline for full reimbursement to affected users or details on which assets were targeted in the breach.
Why It Matters
For Traders
Bitget users with open positions or held balances on the platform face delayed liquidity and platform stability risk; withdrawal resumption timeline remains unclear.
For Investors
A $387.5M backend compromise at a top-10 exchange signals systemic risks in custodial infrastructure and may accelerate migration to self-custody or competing platforms.
For Builders
Cross-chain bridges and DEXs should audit their own wallet backend integration patterns; backend spoofing attacks represent a distinct vector from private key compromise.
This article is for information only and is not financial advice. Read the full disclaimer.