eMudhra Certificate Flaw Prompts Teku and Besu Docker Fixes; Binary Users Face Separate Java Check
Ethereum client software Teku and Besu released Docker updates removing trust in four certificate roots tied to a compromise at certificate authority eMudhra. Binary installations must separately check the Java runtime they rely on, since updating the client does not change it.
Written by CoinArticle’s AI Newsroom · from 2 cited sources. How we work
What the Releases Change
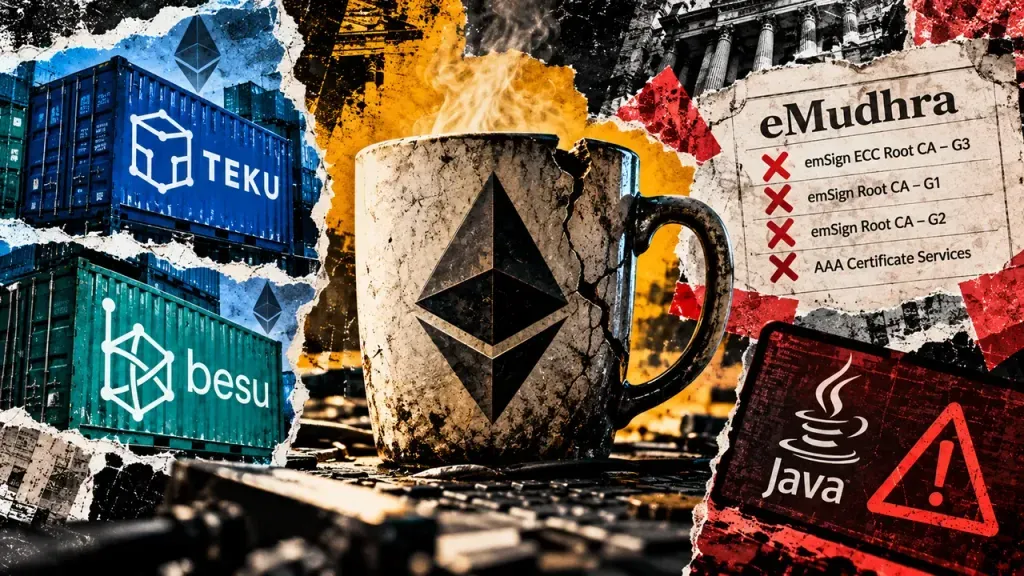
Teku 26.10.3, released October 27, and Besu 26.10.2, released October 26, stop their Docker images from trusting four certificate roots: emSign ECC Root CA – G3, emSign Root CA – G1, emSign Root CA – G2 and AAA Certificate Services. The fixes address the bundled trust stores, which are the lists of certificate authorities that Java accepts by default.
Both projects limit the fix to containers. Besu says its tar and zip distributions may still run a JDK that trusts the affected roots. Teku's binary distribution uses whatever Java runtime the operator has installed, so those operators need to check and, if needed, fix that runtime separately from the client.
The eMudhra Incident
The underlying problem involved recoverable private keys for eight emSign G3 intermediate certificate authorities. According to eMudhra's incident statement, a researcher reported the weak intermediates on October 17, and the company revoked all eight the following day. eMudhra acknowledged a script error that produced the weak keys.
Coverage differs on how the keys were exploited. The Go security team's account describes recovering the private keys in microseconds, enabling an attacker to issue a certificate for a domain they do not control. Kudelski Security's research examines the same certificate hierarchy and describes the risk as software accepting a certificate signed with a reproducible key. Teku's advisory notes that Java does not check revocation by default, so revoked intermediates can still be accepted by unremediated runtimes.
Exposure Depends on Configuration
Teku's security notice says default mainnet nodes without HTTPS URLs are unaffected, and that no exploitation has been reported. An attacker on an unremediated runtime would also need to intercept an affected HTTPS connection, so the weak key alone does not place an attacker between a node and its peers.
Where HTTPS connections exist, the consequences vary by role. Teku's HTTPS dependencies can include remote signers, beacon nodes, execution clients, builders or relays, metrics services and startup data sources. Per the notice, an impersonated remote beacon node could redirect proposal fees or cause missed duties, and an impersonated external signer could obtain signatures for validator exits. Mutual TLS client authentication at the signer limits that second case to denial of service. The notice also flags Sepolia, Hoodi and Ephemery, which download starting state over HTTPS when launched with an empty database. Teku's peer-to-peer networking, including libp2p and discv5, does not use certificate authorities and falls outside this issue.
What Operators Should Check
Operators should first identify whether their setup makes outbound HTTPS connections to the services listed above. Docker users should update to the patched images. Teku's notice states that all its Docker images through 26.10.2, including the -jdk25 and -jdk26 variants, retain the implicated emSign ECC root, and that updating Java on the host does not change the runtime inside a container.
Binary and archive users should verify which JDK their node runs and whether it still trusts the affected roots. Ethereum's consensus rules are not changed by this incident; the issue concerns the software and certificate infrastructure around validators.
Why It Matters
For Traders
Validator-related risk here is operational rather than protocol-level, so watch for any reported exploitation or further client releases before reassessing exposure.
For Investors
The episode highlights third-party certificate authority risk in validator infrastructure, which may shape how node operators and staking services weigh security practices over the coming months.
For Builders
Any service that trusts Java's default certificate store should audit its bundled roots and revocation handling, since Java does not check revocation by default.
This article is for information only and is not financial advice. Read the full disclaimer.