Binance Reports 57 Blocked North Korea-Linked Threats Before $6.34B Hack
Binance said it blocked 57 suspected North Korea-linked cyber threats in 2026, but a staged fake job interview gave attackers access to engineers and wallet-signing systems before the $6.34 billion theft on Oct. 29. The FBI attributed the theft to North Korea's TraderTraitor group, which Pyongyang has denied.
Written by CoinArticle’s AI Newsroom · from 2 cited sources. How we work
Attack Chain Through Recruitment Lures
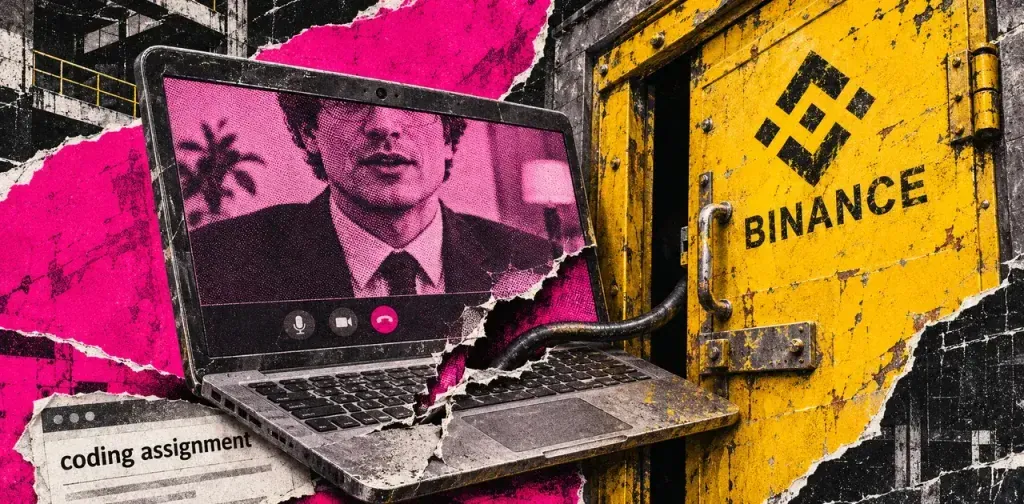
Binance said attackers reached a software engineer in September through a legitimate job-hunting platform, posing as a project director. According to the exchange's Nov. 3 report, a fake human resources representative conducted a video interview, and a second interviewer claiming to be a chief executive asked the engineer to download a coding assignment onto a work computer. The assignment carried malware that ran during setup and evaded the endpoint security tools in use, per Binance.
Co-CEO Yi He's Nov. 3 post on X described the wider pattern: fraudulent job interviews, compromised software packages and browser extensions, fake video conferencing apps, and credential-stealing campaigns. Sources differ on how the intrusion began. Binance's own timeline, as summarized by CryptoSlate, places an earlier stage in June, when a wallet infrastructure engineer installed a tampered Homebrew package while trying to set up an AI coding tool. Binance detected that incident and replaced the device, but Yi's post and the report excerpts available here do not confirm the June event as part of the same chain.
By Oct. 20, attackers had used the compromised machine and an internal AI tool to reach two more engineers. CryptoSlate reports that they obtained a container deployment token and, nine days later, deployed a malicious container to reach wallet-signing infrastructure. Binance said the transfers bypassed its normal withdrawal process and drained assets across several networks.
Wallet Compromise and Authorization Trail
Earlier findings traced part of the loss to Binance 14, an Ethereum hot wallet. Blockaid identified 50 submitted EIP-7702 authorizations, one of which successfully delegated execution rights to a malicious contract. Binance's account and the Blockaid findings describe the same wallet path, though the exchange has not published a full mapping of every authorization to the stolen balance.
Recovery Status and Disputed Figures
Binance said on Nov. 3 that it had replaced 98% of the impacted token assets and was buying the remaining, less liquid tokens. Its figure is higher than the approximately 95% replenishment CEO Richard Teng cited when Bitcoin withdrawals reopened on Nov. 1. The two numbers are not contradictory in principle, since replacement was ongoing, but the exchange has not reconciled them in a single disclosure. Binance said it had set aside more than the funds needed to cover the loss.
Replacement purchases have drawn on the Secure Asset Fund for Users, excess reserves from the Futures Insurance Fund, and corporate treasury, according to earlier recovery disclosures. On Nov. 3, Binance restored withdrawals for 31 more assets on Ethereum and 20 on Solana, following the reopening of five Ethereum stablecoins.
Attribution and Denial
The FBI's Oct. 31 alert, issued with the US Secret Service and IRS Criminal Investigation, attributed the theft to North Korea and named the activity TraderTraitor. Investigators observed the stolen assets being converted primarily into Ether and expected further laundering through decentralized finance and instant swap services. The agencies urged exchanges, analytics firms and DeFi operators to block transactions involving the listed addresses.
North Korea denied involvement on Nov. 3. According to the Associated Press, Kim Yo Jong rejected the accusation in a statement carried by state media. Attribution therefore rests on US government findings, and Pyongyang has not responded to the technical evidence cited.
Pattern Across Recent Operations
The tactics match a campaign security researchers have tracked for some time. The FBI warned in September 2024 that North Korean operators were using tailored job offers and fictional identities against crypto firms. Kudelski Security documented a similar operation, Contagious Interview, in June, in which fake recruiters on LinkedIn, WhatsApp and Discord persuaded developers to run malicious code. Atlassian researchers later reported fake technical assessments on established development platforms. Binance's disclosure shows the same method reaching a major exchange's wallet infrastructure.
Why It Matters
For Traders
Binance's continuing withdrawal reopenings and the 2% of replacement tokens still outstanding are the near-term variables to track for liquidity on affected assets.
For Investors
A $6.34 billion theft attributed to a state actor raises the operational and reserve-adequacy questions that will shape how exchange risk is assessed over months.
For Builders
Attackers exploited EIP-7702 delegation and internal AI tooling, so wallet teams should audit authorization flows and developer tool supply chains now.
This article is for information only and is not financial advice. Read the full disclaimer.