Raydium DEX Loses $1.34 Million in Exploit; Treasury to Cover Loss
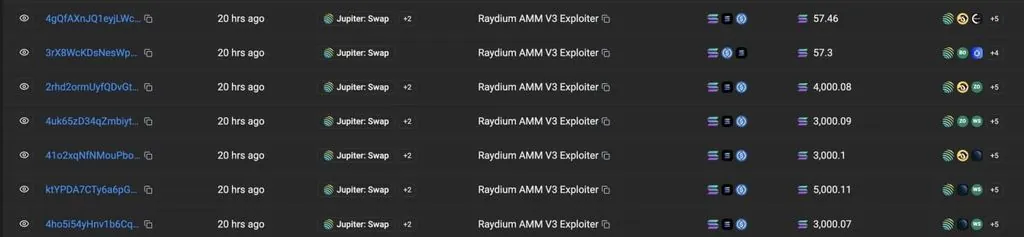
Raydium, a Solana-based decentralized exchange, was exploited for $1.34 million in what security researchers identified as an attack on dormant liquidity pools. The protocol's treasury will reimburse affected users, avoiding forced withdrawals or token dilution.
Written by CoinArticle’s AI Newsroom · from 2 cited sources. How we work
The Exploit and Affected Pools
Raydium suffered a $1.34 million exploit targeting dormant liquidity pools on the Solana network. The attack leveraged unused or abandoned pools within the DEX, according to initial reports. On-chain activity and pool composition data have not yet been made public by the protocol team or independent auditors, limiting transparency into which specific pools were targeted or how the attacker gained access.
Treasury Repayment and Recovery Path
Raydium announced it will cover the full loss using its protocol treasury rather than forcing affected liquidity providers to absorb the loss or executing an emergency token mint. This approach avoids immediate dilution of the RAY token supply and minimizes friction for users with capital locked in the targeted pools. The timeline for full reimbursement and any conditions attached to recovery remain unclear from available statements.
Broader Context for Solana DeFi Security
The exploit underscores persistent vulnerabilities in Solana's DeFi ecosystem despite the chain's speed and low fees. Dormant or low-activity pools—often abandoned as liquidity migrates to newer protocols or higher-fee tiers—present opportunistic attack vectors that may go unmonitored. Whether this incident was due to a smart contract flaw in Raydium's pool logic, a front-running or MEV-related vector, or compromised private keys managing the pools remains undisclosed.
Why It Matters
For Traders
Raydium's swift treasury repayment should prevent liquidity crisis contagion, but the lack of technical disclosure limits confidence in whether similar pools remain at risk.
For Investors
The attack reinforces that Solana DeFi protocols face active security threats; treasury-backed recoveries are unsustainable at scale and erode governance token value over time.
For Builders
Audit focus should shift to dormant or low-TVL pool states; monitoring and emergency pause mechanisms for unused liquidity pairs may become protocol hygiene requirements.
This article is for information only and is not financial advice. Read the full disclaimer.