Attack Injects Crypto-Stealing Code Into 178 Sites, Including Ledger and HSBC
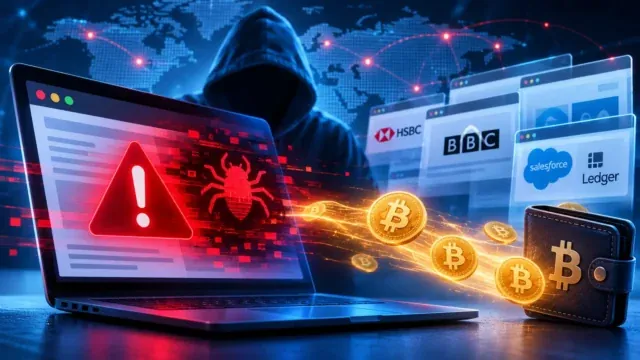
A supply-chain attack planted code on 178 organizations' websites, including HSBC, the BBC, Salesforce and hardware wallet maker Ledger, that could redirect cryptocurrency payments and capture payment card data. Reporting attributes the entry point to a flaw in Optimizely's website optimization platform, and the total amount stolen has not been disclosed.
Written by CoinArticle’s AI Newsroom · from 2 cited sources. How we work
What Happened
Malicious code capable of swapping cryptocurrency destination addresses was planted on 178 organizations' websites, according to reporting from CoinDesk and Bitcoinist. Named targets include HSBC, the BBC, Salesforce and Ledger. The injected code can also collect payment card details and other sensitive information from visitors.
Both outlets trace the entry point to Optimizely, a website optimization platform. CoinDesk describes the initial access as a signup flaw that allowed an attacker to place the code, while Bitcoinist characterizes it as a vulnerability in the platform itself. The two accounts describe the same attack path but frame the weakness differently, and neither report has been confirmed by Optimizely in the material reviewed here.
Scope and Open Questions
The count of affected sites is consistent across both reports at 178. The reports diverge less on scale than on what the attacker has achieved so far. CoinDesk states that the total amount stolen is unknown, and the material reviewed does not identify confirmed losses or specific victims of address redirection.
Whether the campaign involved artificial intelligence is also unresolved. CoinDesk reports that investigators have not linked the attack to AI, and the Bitcoinist piece does not claim such a link.
Why the Vector Matters
The attack works by compromising a third-party script that runs inside a host website, rather than by breaching the host itself. That structure lets one vendor flaw reach many unrelated organizations at once, which is why a single platform can expose a bank, a broadcaster and a hardware wallet maker in the same campaign.
For users, the risk is concentrated at the point of payment or transfer, where a swapped address can send funds to an attacker-controlled wallet without any visible change to the page. Affected organizations would be expected to audit their third-party scripts and review recent page changes, though the sources do not describe remediation steps taken by the named companies.
Why It Matters
For Traders
Users who recently interacted with the named sites should verify wallet addresses before sending funds, since address-swapping code can redirect transfers without visible warning.
For Investors
A single third-party vendor compromise reaching 178 organizations signals that supply-chain security is a material operational risk for custodial and wallet businesses.
For Builders
Any dApp or wallet front end that loads third-party scripts should treat them as a trust boundary and pin, audit, or sandbox them to limit address-swap exposure.
This article is for information only and is not financial advice. Read the full disclaimer.